
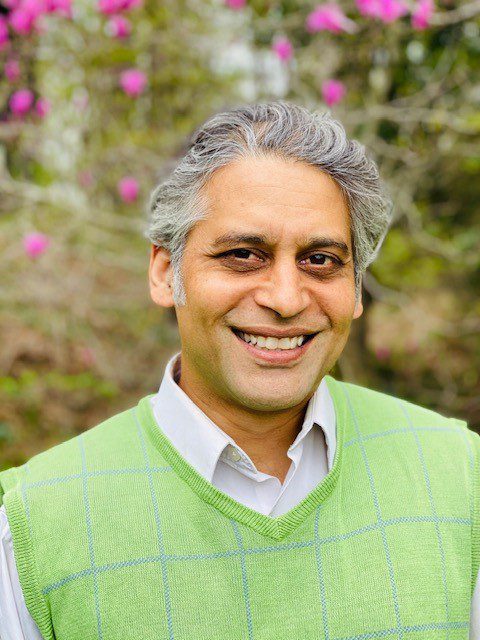
We interviewed Amit Sharma, Head of Digital Strategy at IDEMIA Public Security, who recently joined the Board of Directors at Kantara Initiative. We wanted to know what drives his passion for all things ‘identity’ – and what challenges he sees for the market in general, and the opportunities that may provide for the Kantara community.
- KI: Can you give us a short recap of your experience in the world of digital identity?
AS: I initially cut my teeth at the U.S. Department of Treasury where I worked closely across all of the federal financial regulators in areas specific to Bank Secrecy, risk management and financial crimes compliance. This work revolves around the core question of ‘know your customer (KYC)’, which spurred an interest in the way we manage personal identity information and data. I was particularly interested in how financial services organizations onboard and manage their customers and conduct their regulatory compliance requirements around KYC.
Today, financial services extend well beyond traditional banks. The innovation and advancement of digitally native services, including the constantly evolving financial technology sector with fintech and digital asset service providers, have really challenged regulators. These technologies serve to modernize the applications and enablement that allow consumers and businesses to access financial services products in totally new ways. They also represent a wholesale upgrade of the infrastructure of financial services sector itself. Ensuring that essential regulatory compliance and risk management obligations evolve equally can be challenging—especially when we are working to understand and verify the people and institutions involved.
My key question is how do regulators evolve standards for compliant banking operations so that they can accommodate these new ways of working?
- KI: What is fuelling this interest?
AS: My passion stems from witnessing first-hand the critical role that identity plays in enabling access to essential services and protecting individual rights. The landscape is constantly evolving, which creates both challenges and opportunities to innovate around privacy, security, and user empowerment. I find it incredibly rewarding to contribute to solutions that balance regulatory requirements with positive user experiences—driving a balance between innovative services and ensuring essential consumer protections such as ensuring personal and financial data privacy.
Identity – the mechanisms by which we understand who we are – is the critical element that underpins all regulated services’ obligations to know their customers. I’ve worked for many years on the approach that financial services institutions take to regulatory compliance. And I’ve seen how financial institutions have sought to evolve their processes in the digital era . From traditional organizations such as banks to alternative, innovative services such as decentralized finance (Defi), stablecoins and other forms of digital assets, peer-to-peer payments and other web-native services, all are striving to meet the needs of a digitally native market which is inherently cross-border.
There is huge potential for interoperability between traditional and alternative financial services organizations. And I believe much of this intersection can be unlocked, and secured, through digital identity solutioning; but we’re only just scratching the surface.
- KI: Why do you think standards and certification are so important in the market today?
AS: The more we digitize the sector, the more data we generate, share, and verify, and therefore the more risks emerge. As more consumers and businesses engage with digitally-native services, data sharing and verification processes also change. And therefore so do the threat vectors that can exploit that data, the customer and organizations to whom the data fundamentally belongs. As these new financial services have evolved, the number of risks to personal and financial data has expanded exponentially. Artificial intelligence further exacerbates these vulnerabilities. Proving people are who they say they are in a digital context becomes increasingly difficult with the evolution of synthetic IDs, AI deepfakes and other threats.
Looking at the traditional elements of certification, the standards that Kantara Initiative promotes are already well established in sectors like homeland security, healthcare and criminal justice. But we haven’t seen the same take up in the financial regulatory space. I believe this represents an opportunity both for Kantara Initiative, but also for the wider financial services (FS) market. Standardization in terms of identity verification and evidence through certification is vital in supporting an evolution where tech vendors start looking to interoperability across the identity supply chain. This can also be highly complementary to the underlying obligations that FS providers face from a bank secrecy and regulatory compliance perspective where they are charged to know their customers and ensure they qualify and understand their risk on an ongoing basis. As FS providers evolve beyond traditional banks, personal data management, security, sharing and verification must all equally undertake that rigor.
- KI: Why do you think that financial services organizations have been slow to look to identity standardization?
AS: In the past there’s been a fear of data sharing and interoperability between institutions, This is in part because regulated financial services are under extreme scrutiny from regulators both in terms of how they complete diligence, verify and monitor customers, but also in terms of how they do this across multiple products, services and third-party providers. This has led to financial services institutions working in relative isolation of one another in their own ‘walled gardens’. But new threats in fraud and financial crime such as money laundering, as well as cybercrime, mean that firms recognize the need to become more collaborative and look at developing greater interoperability across the industry. I believe this represents an evolution which can only be enhanced with strong standards that identity service providers must meet.
I’ll give a specific example from the financial services sector. We’ve recently seen the GENIUS Act passed in the US (in July, 2025). This brings a comprehensive regulatory framework for stablecoins—a type of cryptocurrency backed by an underlying asset such as the US Dollar. This legislation reinforces the rise and significance of digital currencies and creates momentum for more innovations and activities in cryptocurrencies and digital assets. Europe has led the market in this area, having already passed similar legislation in the EU more broadly for digital assets.
Separately, Open Banking has been a reality and mandate in Europe for some time but is still finding its feet in the US. This would allow greater freedom for customers to share their financial data securely with third parties (for example to move their account and banking relationships from one organization to another). Truly unlocking account portability, or the sharing of personal financial data between organizations that are also obligated to secure this information, can be challenging.
But this is inherently a challenge of identity.
To be fully onboarded at a new organization, I still have to present my identity credentials, including Personal Identity Information (PII) and other relevant personal data to enable that organization to fulfil its KYC obligations. With digital identities and verifiable credentials, I could instead simply share them with the relevant parties (e.g. the new bank or fintech organization) who could in-turn verify me without my having to resubmit my personal data. The previous institution would have already verified my details.
However, for this to happen, we need full interoperability of the technology used by both organizations, with both parties fully confident that everything meets the most rigorous of data standards. All parties must be able to trust that any technology that carries out the verification, sharing and storage of personal data and credentials is compliant with a trustworthy set of standards for identity. This requires a level of transparency that common certification can bring.
If we already have standards for interoperability in other sectors and domain spaces, we should equally facilitate this within financial services.
- KI: Are there are issues around privacy that are not yet fully explored?
AS: This is an area where I feel personally very passionate – never mind that it’s also an area that regulators also get very passionate about! Right now, the bank, insurer, broker “own”—if not control— our personal data. But we don’t necessarily have to live in that world. This may have made sense with analogue systems where we didn’t have the kind of privacy enhancing technologies and verifiable credentials we have today. It is now possible to hold our own data and credentials and share just what is needed without having to disclose everything time and time again. Not every process requires the FS provider to see the underlying data—they simply need to verify that the essential identity attributes and KYC information is in fact valid, current and verifiable.
It’s a concept I’ve been pressing for through my work in previous organizations and carry forward with IDEMIA Public Security. About a year ago we went to the Consumer Financial Protection Bureau (CFPB) and suggested they look at the opportunities that exist with decentralized identity and verifiable credentials. These will better facilitate mandates such as Open Banking. We helped them reference such capabilities within the 1033 rule of the Dodd Frank Act, which allows consumers to access and share their personal financial data with different service providers at no charge. These customers would then be assured that any Identity data or credentials that have been digitally verified could be shared onwards with any new financial institution for the purposes of KYC, AML or anti-fraud protection. The use of digital identities and verifiable credentials that affirm the veracity of underlying identity information is a strong way to facilitate secure information sharing, and would unlock Open Banking in a secure and privacy-enabled environment.
Suddenly the barriers to fast customer onboarding are removed. I can port my data from institution to institution, from account to account. It’s a bit like porting my cell phone data and number when I travel from country to country without having to share that data with each telecoms provider. It should be equally easy to port my personal and financial data to access services in a rapidly evolving and global financial services ecosystem.
In addition, fraud, identity theft and account takeover tools are enhanced as personal identifying information (PII) is not constantly exposed and therefore vulnerable to human error or bad actors.
- KI: What do you think is the best role Kantara Initiative can play in this new world?
AS: The work that Kantara Initiative does is fundamental to the efforts we have been discussing. Firstly, it brings people together – cross sector, buyers and vendors – to debate core issues of common concern, especially as they relate to fraud and identity threats as well as their regulatory obligations around KYC activities. The Kantara community considers core challenges related to identity threats, interoperability and regulatory compliance and looks at these through different lenses such as Deep Fakes and other AI threats, financial exclusion or considerations as to how assurance criteria evolve to ensure compliance with the new NIST or other Trust Framework guidelines.
I can envision how Kantara Initiative might bring financial institutions together to look at interoperability mechanisms that meet common concerns that are specific to regulated financial services. With common standards, we can all be confident that any individual’s identity has been verified in a truly trustworthy way and then shared across an evolving and growing financial services ecosystem in keeping with common consumer protection and bank secrecy goals. This also stands true for peer-to-peer, crypto or other digital transactions that are increasingly innovated with and among traditional services.
Basically, we want to verify once and then use and reuse many times in a secure way that enables consumers to reclaim control of their identity data.
In the past, a bank or other “relying party” has been nervous about trusting the data verification process to other organizations or third parties. But now, if all the various vendors and technologies meet a consistent set of standards, we can facilitate secure, compliant and more efficient and cost effective identity verification and KYC. This becomes a major consideration with the cost of compliance for many banks at around 25-30% of their operating budgets. It also helps address the millions of dollars lost to fraud and other challenges.
As long as all the various tools across the identity ecosystem can demonstrate compliance to the latest digital identity and financial regulation standards, there should be no need for silos to exist. Kantara Initiative makes sure these standards are all fit for purpose and align to any new regulations or guidelines.
Ultimately, interoperability will massively improve efficiency, and privacy can also be reinforced.
The technology exists. The standards exist. But we need diverse financial services providers and the new digital platforms, exchanges etc to step up and engage in collaborative solutions. We need a focus on interoperability as this will also provide confidence to financial regulators and supervisors when they see consistent approaches to compliance.
It makes sense from a customer perspective.
It makes sense from a regulatory perspective.
And it makes sense from an efficiency and profitability perspective.
But most of all, it makes sense from a consumer empowerment and privacy perspective. Ultimately, this will fuel greater trust across the whole sector. And that is something that should remain a focus for all of us from tech vendors to regulators, standards bodies and consumer agencies.